
Ransomware vs. Data Backups: Why You Need Both
When practice managers evaluate threat mitigation, establishing robust ransomware protection in Edmonton AB is vital to operational survival. Many local business leaders operate under a dangerous misapprehension. Specifically, they assume that simply maintaining nightly data backups makes their business immune to ransomware. Unfortunately, modern cybercriminals have evolved far beyond basic file encryption. Consequently, unprepared practices face catastrophic data loss, operational paralysis, and severe regulatory penalties.
During local infrastructure audits of Edmonton practices, engineering teams routinely uncover critical gaps in disaster recovery planning. Organizations frequently rely on unencrypted local drives. Furthermore, they execute unverified backups, or fail to isolate recovery repositories from the primary network. As a result, a single targeted attack can compromise active systems and historical backup snapshots simultaneously.
To help managing partners, practice directors, and executive teams safeguard their digital assets, this guide analyzes network vulnerabilities. Therefore, we explore why data backups alone cannot stop cyberattacks. Finally, we highlight why true business resilience requires integrated ransomware protection in Edmonton AB.
Understanding the Evolution of Modern Ransomware Attacks
In early cyberattacks, malicious software simply encrypted local files and demanded a payment for the decryption key. Under that legacy threat model, restoring files from an uninfected off-site backup was highly effective. For instance, it allowed a business to recover without paying the extortion fee. However, modern cybercrime syndicates now execute multi-stage double and triple extortion attacks. These advanced methods are specifically designed to neutralize traditional backups.
The Double and Triple Extortion Model
- Data Exfiltration Before Encryption: Before encrypting a single hard drive, attackers silently exfiltrate sensitive client financial records. Moreover, they steal employee personal data, or patient health information. If a business restores its network using backups and refuses to pay the ransom, criminals deploy new threats. Specifically, they threaten to publish the stolen data publicly or sell it on the dark web.
- Targeted Backup Destruction: Threat actors deliberately spend days or weeks inside a compromised network mapping out backup infrastructure. They locate cloud sync tools, delete volume shadow copies, and wipe online backup repositories before initiating encryption.
- Downstream Regulatory Extortion: Attackers directly contact the clients, patients, or regulatory bodies of the victimized practice. For example, they may contact the Office of the Information and Privacy Commissioner of Alberta (OIPC). Consequently, they report the security breach directly, multiplying legal and reputational pressure.
Practices seeking to fortify their defense against these complex threats can deploy dedicated cybersecurity services in Edmonton to secure every layer of their network infrastructure.
Why Backups Alone Cannot Prevent Operational Failure
While data backups are an essential component of business continuity, relying on them as a standalone security strategy is highly risky. Specifically, it exposes Edmonton firms to critical vulnerabilities and extended downtime.
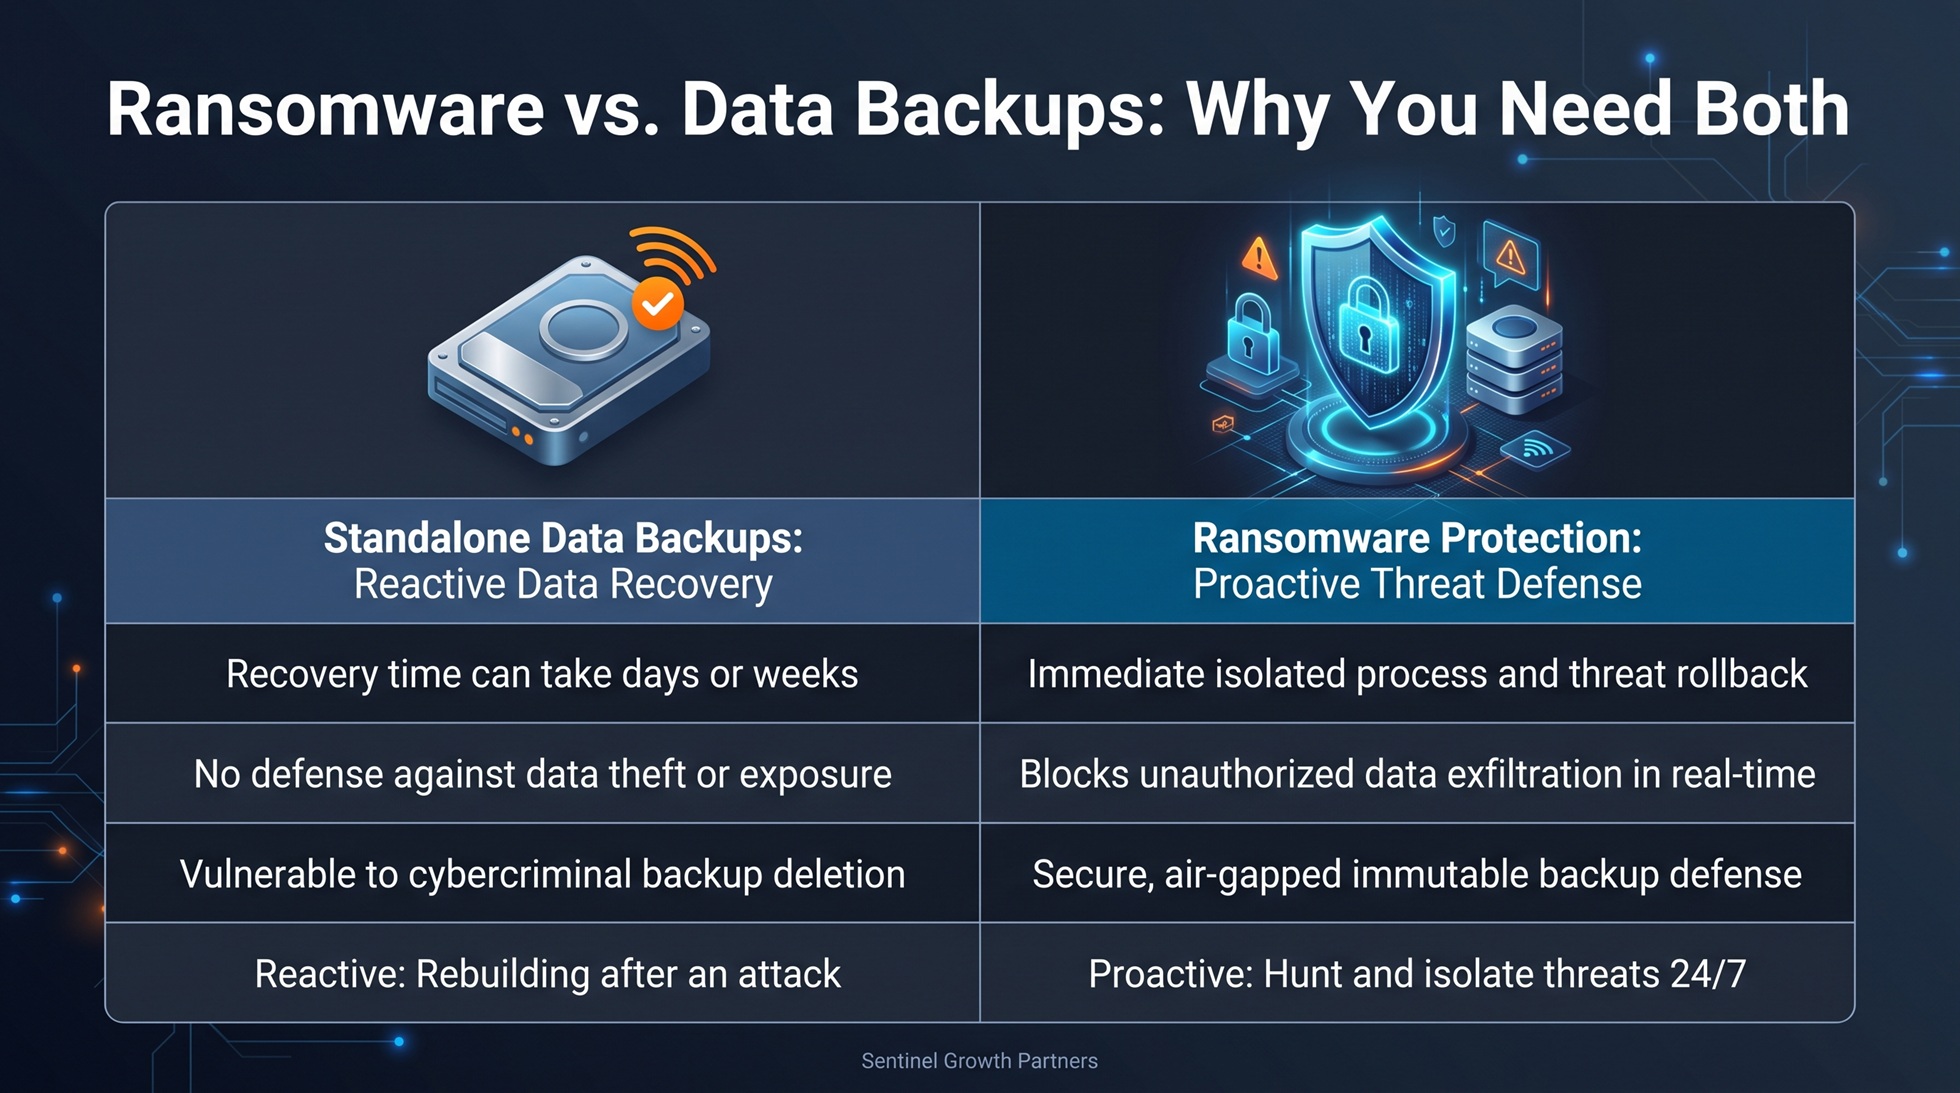
Comparing Backups and Proactive Defense Mechanisms
| Feature | Standalone Data Backups | Proactive Ransomware Protection in Edmonton AB |
| Data Loss Prevention | Does not prevent data exfiltration or theft. | Blocks unauthorized data exfiltration in real time. |
| Threat Detection | Zero capability to detect active network intrusions. | Uses AI-driven EDR to detect and isolate threats immediately. |
| Recovery Speed | Hours or days required to rebuild infrastructure. | Near-instant endpoint isolation and automated process rollback. |
| Regulatory Protection | Does not prevent mandatory OIPC breach reporting. | Enforces Zero-Trust access to maintain HIA/PIPA compliance. |
The Hidden Costs of Unprotected Restores
Restoring an entire enterprise network from raw data backups is rarely a fast or seamless process. Even with verified cloud snapshots, rebuilding domain controllers takes significant time. Furthermore, reconfiguring line-of-business software, and verifying file integrity can take days or weeks. During this prolonged outage, law firms cannot access court filings. Likewise, accounting practices miss critical tax deadlines, and medical clinics are forced to turn away patients.
Furthermore, if the original security vulnerability is not identified and remediated prior to restoring files, severe risks remain. Cybercriminals can simply re-trigger the ransomware executable the moment systems come back online. Therefore, a reactive strategy is never sufficient.
Core Components of Ransomware Protection in Edmonton AB
True digital resilience requires combining air-gapped data backups with real-time threat hunting and active defense protocols. Implementing comprehensive ransomware protection in Edmonton AB ensures that malicious actors are blocked completely. As a result, they are stopped long before they reach your sensitive data repositories.
Secure Perimeter and Backup Architecture
- Zero-Trust Architecture and MFA: Enforce Multi-Factor Authentication (MFA) across all remote access points, email accounts, and administrative portals. Zero-Trust access policies ensure that compromised credentials alone cannot grant access to core server infrastructure.
- Air-Gapped Immutable Backups: Maintain immutable backup snapshots that cannot be modified, encrypted, or deleted. Consequently, no user or automated script on the network can alter them. Storing copies off-site in secure Canadian data centers ensures complete data sovereignty under provincial privacy laws.
- Endpoint Detection and Response (EDR): Deploy AI-powered EDR agents across all workstations and servers. Modern EDR tools continuously monitor system processes. Therefore, they automatically freeze unauthorized encryption attempts and roll back damaged files instantly.
- Email Security and DMARC Enforcement: Implement strict email authentication protocols (SPF, DKIM, DMARC) to prevent spear-phishing attacks. Phishing emails represent the primary entry vector for ransomware delivery.
Firms planning an infrastructure upgrade or commercial relocation can consult our guide on managed IT services in Edmonton to build a resilient, multi-layered environment.
Actionable Steps to Secure Your Practice Against Ransomware
Securing your business requires a coordinated, proactive methodology that bridges technical safeguards and administrative governance. Relying on outdated methods will not protect your assets. Therefore, upgrading to modern ransomware protection in Edmonton AB is critical.
Governance and Isolation Tactics
- Audit Backup Isolation: Verify that your primary backup repositories are strictly isolated. They must remain separate from standard user network segments and domain controller credentials.
- Conduct Annual Recovery Simulations: Perform regular restoration drills to measure actual Recovery Time Objectives (RTO). Furthermore, measure Recovery Point Objectives (RPO) under simulated disaster conditions.
- Enforce Strict Least-Privilege Access: Restrict user permissions aggressively. Employees should only access the specific drives and databases necessary for their immediate daily tasks.
- Establish Continuous Vulnerability Management: Regularly patch operating systems, firewalls, and third-party software. Consequently, this helps to eliminate known security vulnerabilities.
- Partner with Local Security Experts: Work with dedicated technical partners who provide 24/7 network monitoring. Additionally, they must provide rapid on-site incident response.
To discover how your current network measures up against modern cyber threats, visit our about page to learn about our proactive vCIO risk management.
The Reality of Ransomware Protection in Edmonton AB
Cybercriminals no longer target just enterprise corporations. Today, they actively hunt local professional practices because they possess highly valuable data and often lack enterprise-grade defenses. Without modern ransomware protection in Edmonton AB, your practice remains a highly lucrative target.
Do not assume your current IT provider is actively monitoring for advanced threats. Many traditional helpdesks only react when a server goes down or a user submits a support ticket. By that point, the ransomware encryption process is usually complete. Proactive security requires active, 24/7 threat hunting and continuous vulnerability patching.
Claim Your Free Infrastructure Security Audit
Do not wait for a security breach to discover vulnerabilities in your disaster recovery plan. Sentinel Growth Partners offers a complimentary, non-invasive 15-Point Cybersecurity & IT Infrastructure Audit tailored for Edmonton practices.
Our comprehensive audit evaluates:
- Email authentication protocols (SPF, DKIM, DMARC validation)
- Public IP exposure and open firewall ports
- Dark web scanning for compromised employee credentials
- Backup isolation and SSL certificate health
Leave a Reply